AWS Security Blog

How to deploy CloudHSM to securely share your keys with your SaaS provider
August 31, 2021:AWS KMS is replacing the term customer master key (CMK) with AWS KMS key and KMS key. The concept has not changed. To prevent breaking changes, AWS KMS is keeping some variations of this term. More info. August 6, 2019: We’ve made an update to clarify use cases for VPC peering. If your […]

How to migrate a digital signing workload to AWS CloudHSM
Feb 17, 2025: This blog post references AWS CloudHSM Client SDK 3, which is no longer the recommended version. AWS recommends that you use the latest version, AWS CloudHSM Client SDK 5, which provides updated functionality and commands. We are currently working on an updated blog post for CloudHSM Client SDK 5. See the AWS […]

How to set up an outbound VPC proxy with domain whitelisting and content filtering
May 12, 2025: We’ve updated the CloudFormation template to use a launch template instead of a launch configuration. November 16, 2020: We’ve updated the CloudFormation template and the launch stack URL used in this solution. July 24, 2019: We’ve added a link to a GitHub repository that contains the stack content for this solution. Controlling […]

Introducing the AWS Security Incident Response Whitepaper
April 25, 2023: We’ve updated this blog post to include more security learning resources. AWS recently released the AWS Security Incident Response whitepaper, to help you understand the fundamentals of responding to security incidents within your cloud environment. The whitepaper reviews how to prepare your organization for detecting and responding to security incidents, explores the […]

New! Set permission guardrails confidently by using IAM access advisor to analyze service-last-accessed information for accounts in your AWS organization
You can use AWS Organizations to centrally govern and manage multiple accounts as you scale your AWS workloads. With AWS Organizations, central security administrators can use service control policies (SCPs) to establish permission guardrails that all IAM users and roles in the organization’s accounts adhere to. When teams and projects are just getting started, administrators […]

How to host and manage an entire private certificate infrastructure in AWS
AWS Certificate Manager (ACM) Private Certificate Authority (CA) now offers the option for managing online root CAs and a full online PKI hierarchy. You can now host and manage your organization’s entire private certificate infrastructure in AWS. Supporting a full hierarchy expands AWS Certificate Manager (ACM) Private Certificate Authority capabilities. CA administrators can use ACM […]

How to prompt users to reset their AWS Managed Microsoft AD passwords proactively
If you’re an AWS Directory Service administrator, you can reset your directory users’ passwords from the AWS console or the CLI when their passwords expire. However, you can improve your efficiency by reducing the number of requests for password resets. You can also help improve the security of your organization by having your users proactively […]
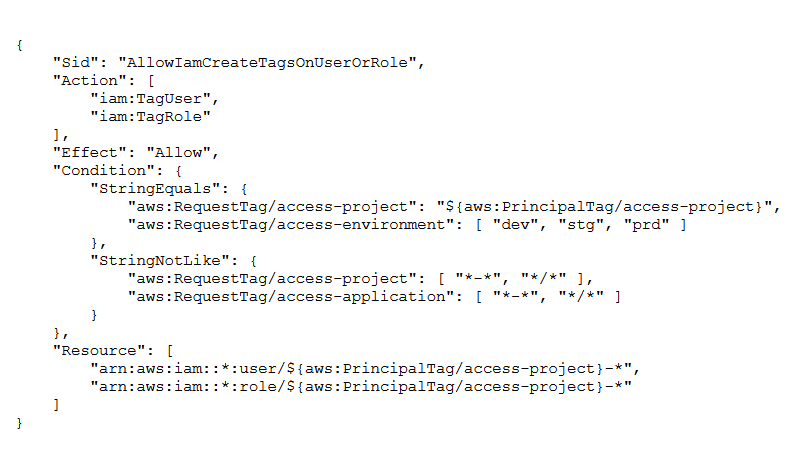
Working backward: From IAM policies and principal tags to standardized names and tags for your AWS resources
February 11, 2021: We updated the tag and instance creation policies for Amazon EC2 to reflect network interface support for attribute-based access control (ABAC). We also added a link to additional sample policies for launching an EC2 instance, and we corrected a condition key “aws:RequestTag/access-zone” to “aws:RequestTag/access-environment”. Amazon ElastiCache now supports names up to 50 […]

Definitely not an AWS Security Profile: Corey Quinn, a “Cloud Economist” who doesn’t work here
In the weeks leading up to re:Inforce, we’ll share conversations we’ve had with people who will be presenting at the event so you can learn more about them and some of the interesting work that they’re doing. You don’t work at AWS, but you do have deep experience with AWS Services. Can you talk about […]

AWS Security Profiles: Fritz Kunstler, Principal Consultant, Global Financial Services
Photo courtesy of Fritz Kunstler In the weeks leading up to re:Inforce, we’ll share conversations we’ve had with people at AWS who will be presenting at the event so you can learn more about them and some of the interesting work that they’re doing. How long have you been at AWS, and what do you […]